Goddess of Victory: NIKKE PC launcher hit by supply-chain attack
Reports indicate that the PC launcher for Goddess of Victory: NIKKE was compromised in a supply-chain attack, potentially exposing players to malicious code. According to a timeline compiled by community members on the Chinese forum NGA and published via GitHub, attackers injected malware into four JavaScript files hosted on Level Infinite’s official CDN starting September 27. These files are loaded when the launcher opens.
The malicious code reportedly began installing a remote-access agent on user computers from October 24 onward. This agent granted extensive system access, including the ability to execute commands, browse files, take screenshots, and steal credentials such as SSH keys and cryptocurrency wallet data. The infection did not occur on every launch, affecting only some users.
As of November 3, three of the four compromised files had been replaced, though two CDN servers still distributed modified versions. No official confirmation has been issued by developer Shift Up or publisher Level Infinite. Players are advised to avoid launching the game until the issue is resolved and to clear their cache.
Summary written with AI assistance by the Hentaidude News Desk from the original report by Amber V at AUTOMATON WEST and checked by our automated quality rules. Details may change; see the source for the full story. How we write summaries
Original headline at AUTOMATON WEST: “Goddess of Victory: NIKKE PC launcher reportedly compromised in supply-chain attack. No official confirmation from developers yet”
Key facts
- Developer
- Shift Up
- Publisher
- Level Infinite
- Platform
- PC
Tags
- #Goddess of Victory: NIKKE
- #Level Infinite
- #PC Game
- #Security Breach
- #Shift Up
- #Supply-Chain Attack
Background
Earlier stories from our archive that give context to this one.
Related stories
More games: Related stories
Comic CMOA Partially Restarts After Security Breach
Partial service resumed on October 29; service has been down since October 15 due to unauthorized external access
via Anime News Network
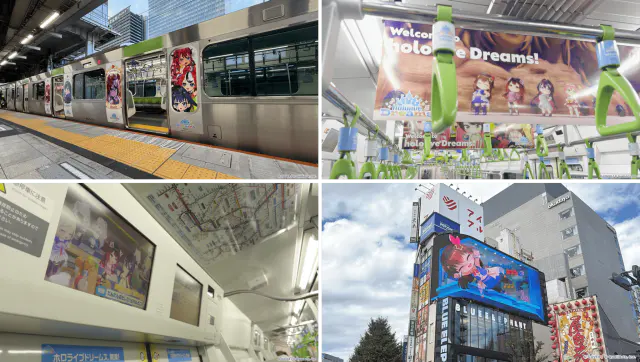
hololive Dreams Global Advertising Campaign Hits Seven Cities
The campaign covered seven cities: Osaka, Taipei, Seoul, Jakarta, Los Angeles, New York and Tokyo.
via AniTrendz
Azur Promilia Asian Release Set for November 26
The Azur Promilia release date is set for China, Japan, South Korea, and Taiwan, and there's a new trailer and character to see.
via Siliconera
Roco Kingdom Quack Quack Beta Test Begins October 27
People can check Roco Kingdom Quack Quack beta test status, pre-download the game and watch a gameplay trailer.
via Siliconera
Enish Announces DanMachi Frontier Zero Game for 2027
New game with original story cooperation by creator Fujino Ōmori planned for release on iOS, Android, PC inside, outside Japan
via Anime News Network
New Supernatural Murder Mystery Angelic Agency Coming to Steam
An indie developer invokes the spirit of two legendary supernatural horror IPs to create a thrilling new game about detectives who deal with ghosts.
via CBR Anime