Good Smile Company Data Breach Compromises Credit Card Details of 2,800 Customers
Good Smile Company has confirmed that a security breach affecting its online store potentially exposed the full credit card information of approximately 2,800 customers. The Japanese developer and toy manufacturer announced on October 29 that unauthorized access occurred between October 19 and October 22, leading to the temporary closure of its website. The compromised data includes cardholder names, complete card numbers, expiration dates, and security codes.
The company clarified that this incident is unrelated to the recently reported PHP vulnerability issue. Instead, it appears a third party exploited a system weakness to gain administrative privileges. Good Smile Company is individually contacting all affected users via email with further details. While over 400,000 cards may have been partially leaked, the full compromise applies specifically to the smaller group of 2,800 individuals who interacted with payment systems during the breach window.
Summary written with AI assistance by the Hentaidude News Desk from the original report by Đorđe P at AUTOMATON WEST and checked by our automated quality rules. Details may change; see the source for the full story. How we write summaries
Original headline at AUTOMATON WEST: “Good Smile Company reports potential leak of full credit card information of 2,800 customers in major data breach”
Key facts
- Affected Customers (Full CC)
- Approximately 2,800
- Breach Window Start
- October 19 at 3:00 PM
- Breach Window End
- October 22 just before 11:00 PM
- Website Closure Date
- October 23
- Update Announcement Date
- October 29
Tags
- #Credit Card Leak
- #Cybersecurity
- #Data Breach
- #Good Smile Company
- #Online Store
Background
Earlier stories from our archive that give context to this one.
Related stories
More games: Related stories
Good Smile Company Data Breach Exposes Credit Card Details
Company's current update states customers' complete 16-digit card number may have been exposed due to breach
via Anime News Network
Good Smile Company Data Breach Exposes Up to 2,800 Customers’ Credit Cards
Japanese figure manufacturer Good Smile Company has revealed that a major cyberattack on its official online store may have compromised the complete credit card information of approximately 2,800 customers, including card numbers, expiration dates, and security codes.
via Sankaku Complex
Takanori Nishikawa Releases Dandivine Opening Song Music Video
Crunchyroll is streaming the new anime series
via Crunchyroll News
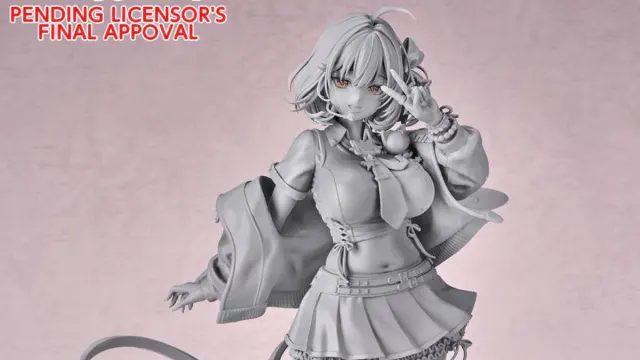
NIKKE 4th Anniversary Web Event Live; Anis Figure Teased
A refresher Goddess of Victory: NIKKE 4th anniversary web event is live and there's a teaser for a pop star Anis figure.
via Siliconera
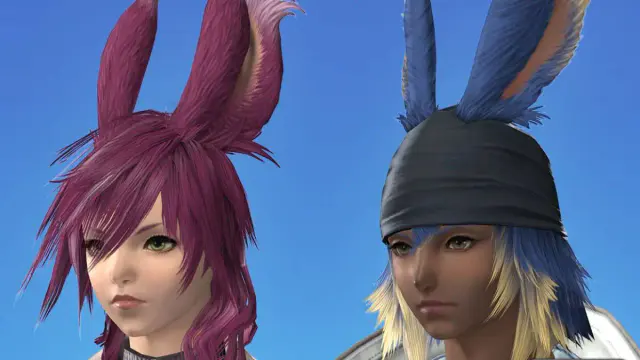
FFXIV Online Store Sells Modern Aesthetics Haircuts Separately
It is possible to get FFXIV Online Store Modern Aesthetics hairstyles alone instead of hair cuts only being sold with costumes.
via Siliconera
Japanese Cloud Cyberattack Disrupts Digital Manga Access
As one of Japan's biggest cloud firms is hit with a cyberattack, eBook readers are given a grim reminder of the accessability of their books in situations like this.
via Anime UK News